
CMMC compliance solution
CMMC compliance solutions that show proof
Netwrix CMMC compliance solutions give you continuous visibility into who can reach controlled unclassified information (CUI), enforce least privilege, and produce the dated, attributed evidence a C3PAO asks for.
Most compliance software can't tell you who actually has access to CUI, or prove it to an assessor.
You can't scope what you can't see
55% of organizations don't continuously maintain a sensitive data inventory, and CMMC scoping starts with knowing where CUI lives (2026 Data and Identity Security Report).
Access outlasts the need
76% of organizations can't immediately revoke standing access when it's no longer needed, and CMMC asks for least privilege, including for privileged accounts (same report).
Risk assessments stay shallow
Only 36% of organizations conducted a comprehensive Active Directory security assessment in the last 12 months, and only 26% are fully confident their Active Directory is free of misconfigurations that could enable privilege escalation (same report).
CMMC compliance solutions from Netwrix: what CMMC 2.0 Level 2 requires and how we help
Netwrix Auditor deploys in 30 minutes, with first reports within hours.
Requirement
What CMMC requires
Netwrix
NIST SP 800-171 3.1.3, Access Control
Control the flow of CUI in accordance with approved authorizations.
Data Classification classifies CUI by severity across servers, databases, and folders and, working with Auditor, allows access only to authorized users.
NIST SP 800-171 3.1.5, Access Control
Employ the principle of least privilege, including for specific security functions and privileged accounts.
Privilege Secure removes standing privileged accounts and grants just-in-time access with only the privileges the session needs, then records the session.
NIST SP 800-171 3.3.2, Audit and Accountability
Ensure that the actions of individual system users can be uniquely traced to those users, so they can be held accountable for their actions.
Auditor shows which user did what, when, and where across Active Directory, Entra ID, file servers, and other systems that hold CUI, and keeps a profile for each registered user.
NIST SP 800-171 3.4.1, 3.4.2, Configuration Management
Establish and maintain baseline configurations of organizational systems, and establish and enforce security configuration settings.
Change Tracker defines baselines for software and configuration, detects systems that drift from them, and produces certified CIS and DISA STIG hardening reports.
NIST SP 800-171 3.11.1, Risk Assessment
Periodically assess the risk to organizational operations, assets, and individuals from the systems that process, store, or transmit CUI.
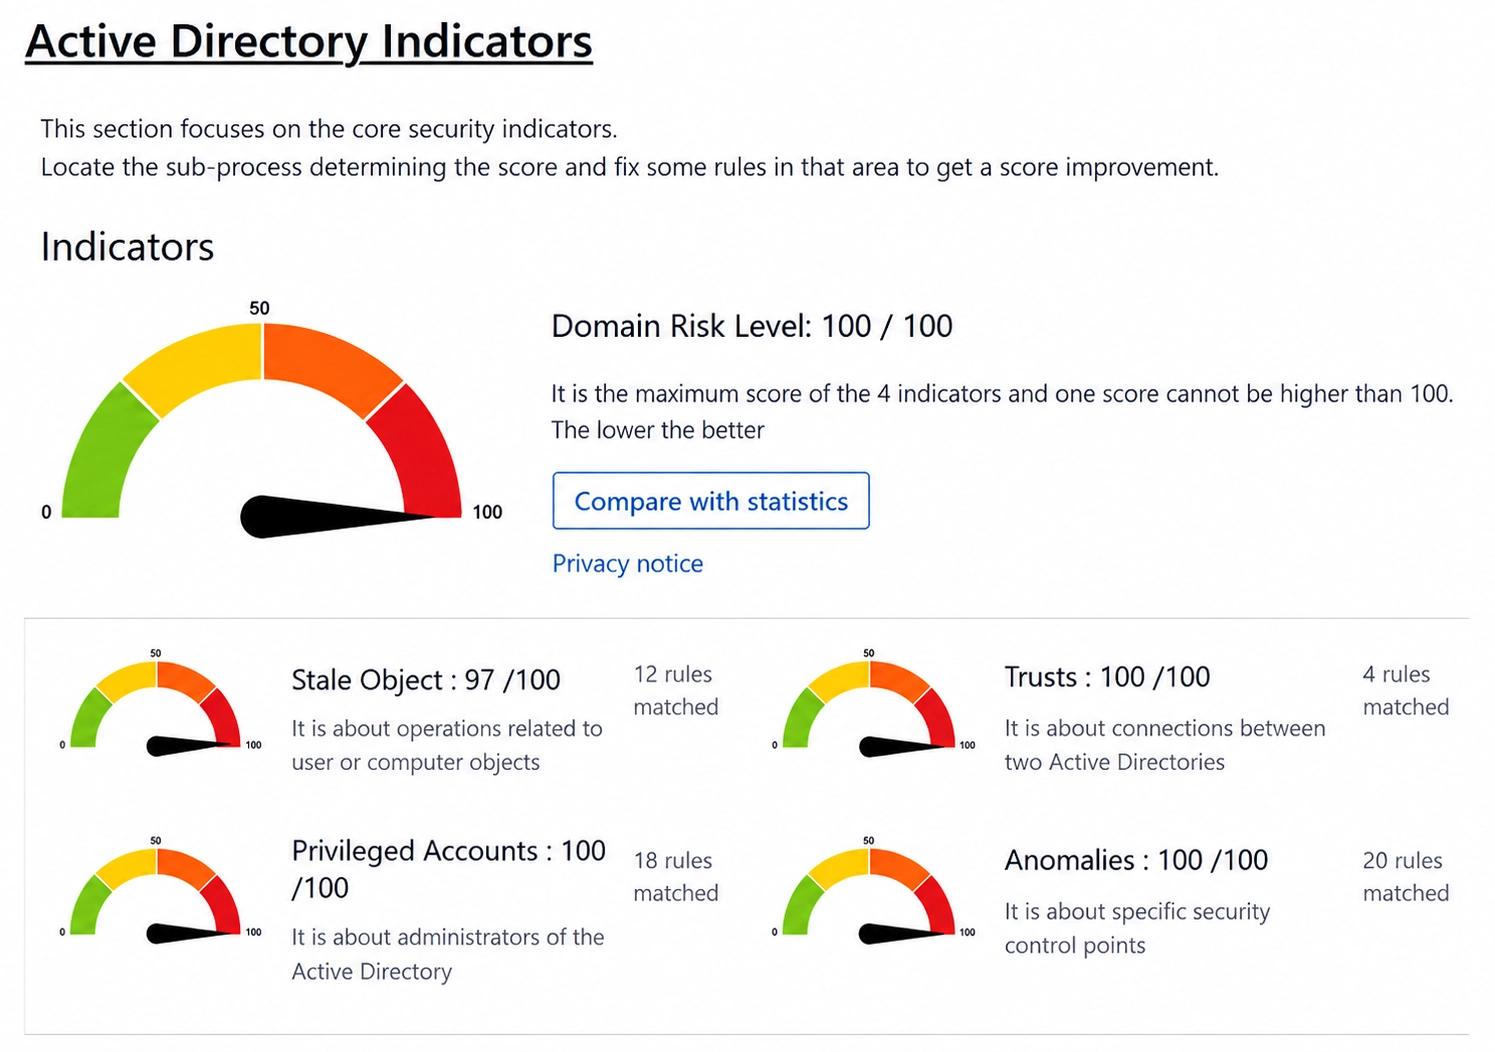
PingCastle generates Active Directory health checks, risk scores, and action plans, and tracks remediation progress.
NIST SP 800-171 3.11.2, Risk Assessment
Scan for vulnerabilities in organizational systems and applications periodically and when new vulnerabilities are identified.
Access Analyzer highlights risks to sensitive data, such as open access or too many users with privileged access, and helps remediate them at scale by cleaning up stale objects.
NIST SP 800-171 3.8.7, Media Protection
Control the use of removable media on system components.
Endpoint Protector controls which removable devices can connect, encrypts files copied to approved USB storage, and reports on attempted and blocked transfers.
See the full CMMC-to-portfolio mapping
See it in action
Track every log-in to systems that hold CUI
See who logged in, when, where, and to which computer, so unusual log-in activity on systems that hold CUI can be spotted and reported quickly.
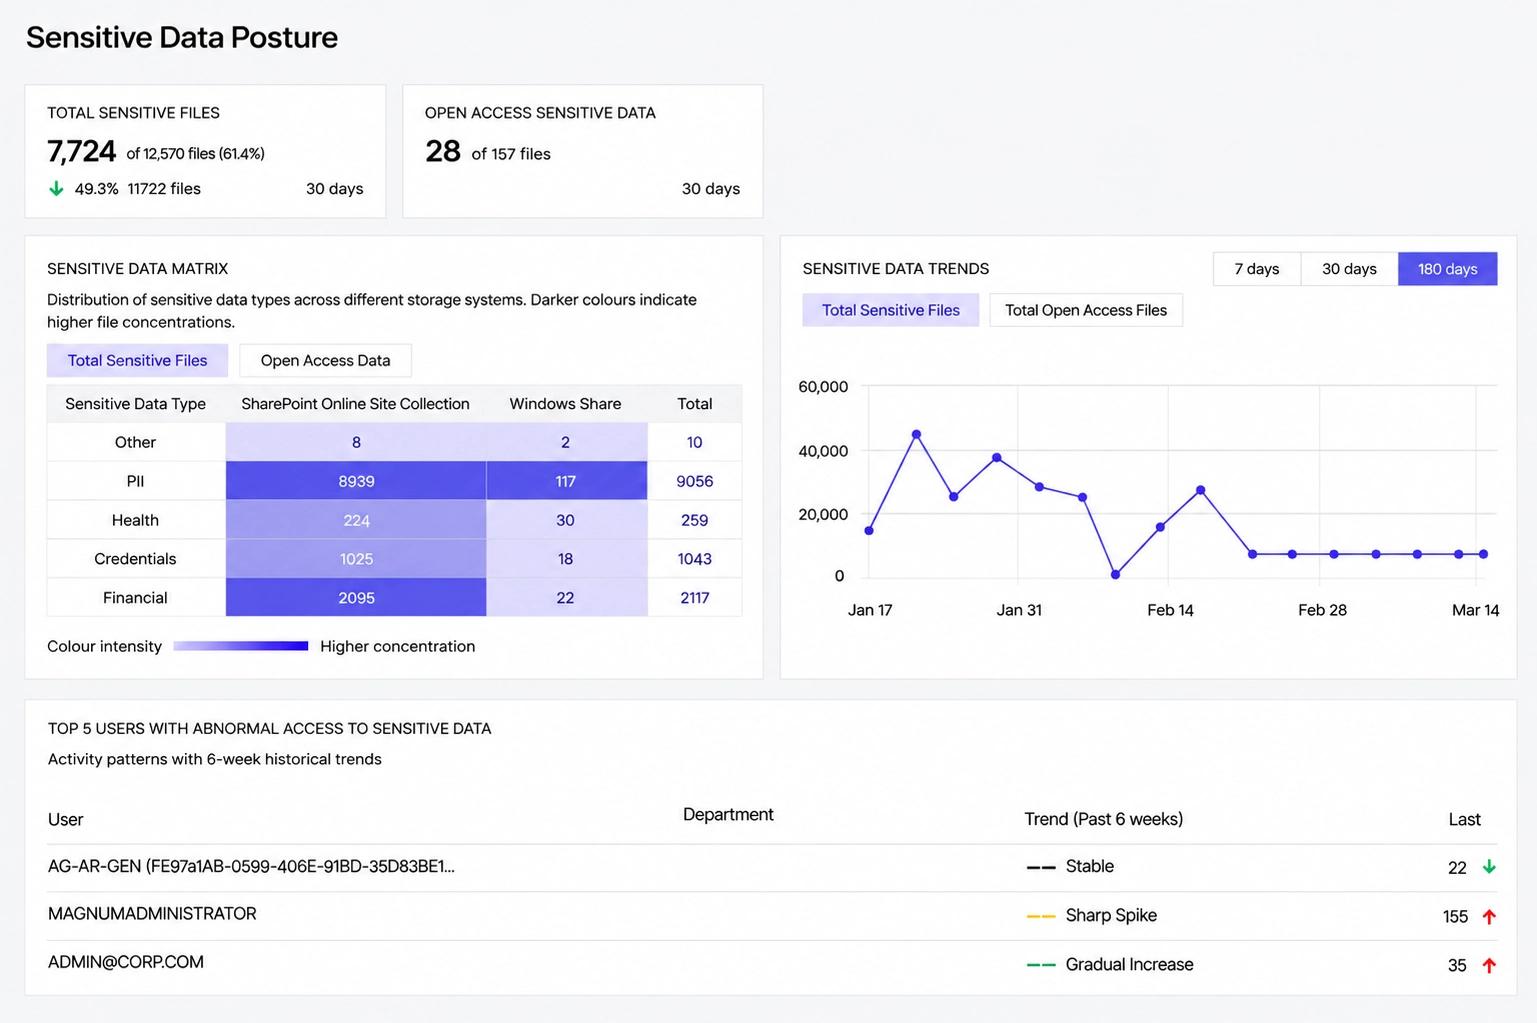
Let data owners review who can reach CUI
Entitlement reviews put access decisions in front of the people who own the data, so every right to CUI is reviewed, approved, and documented.
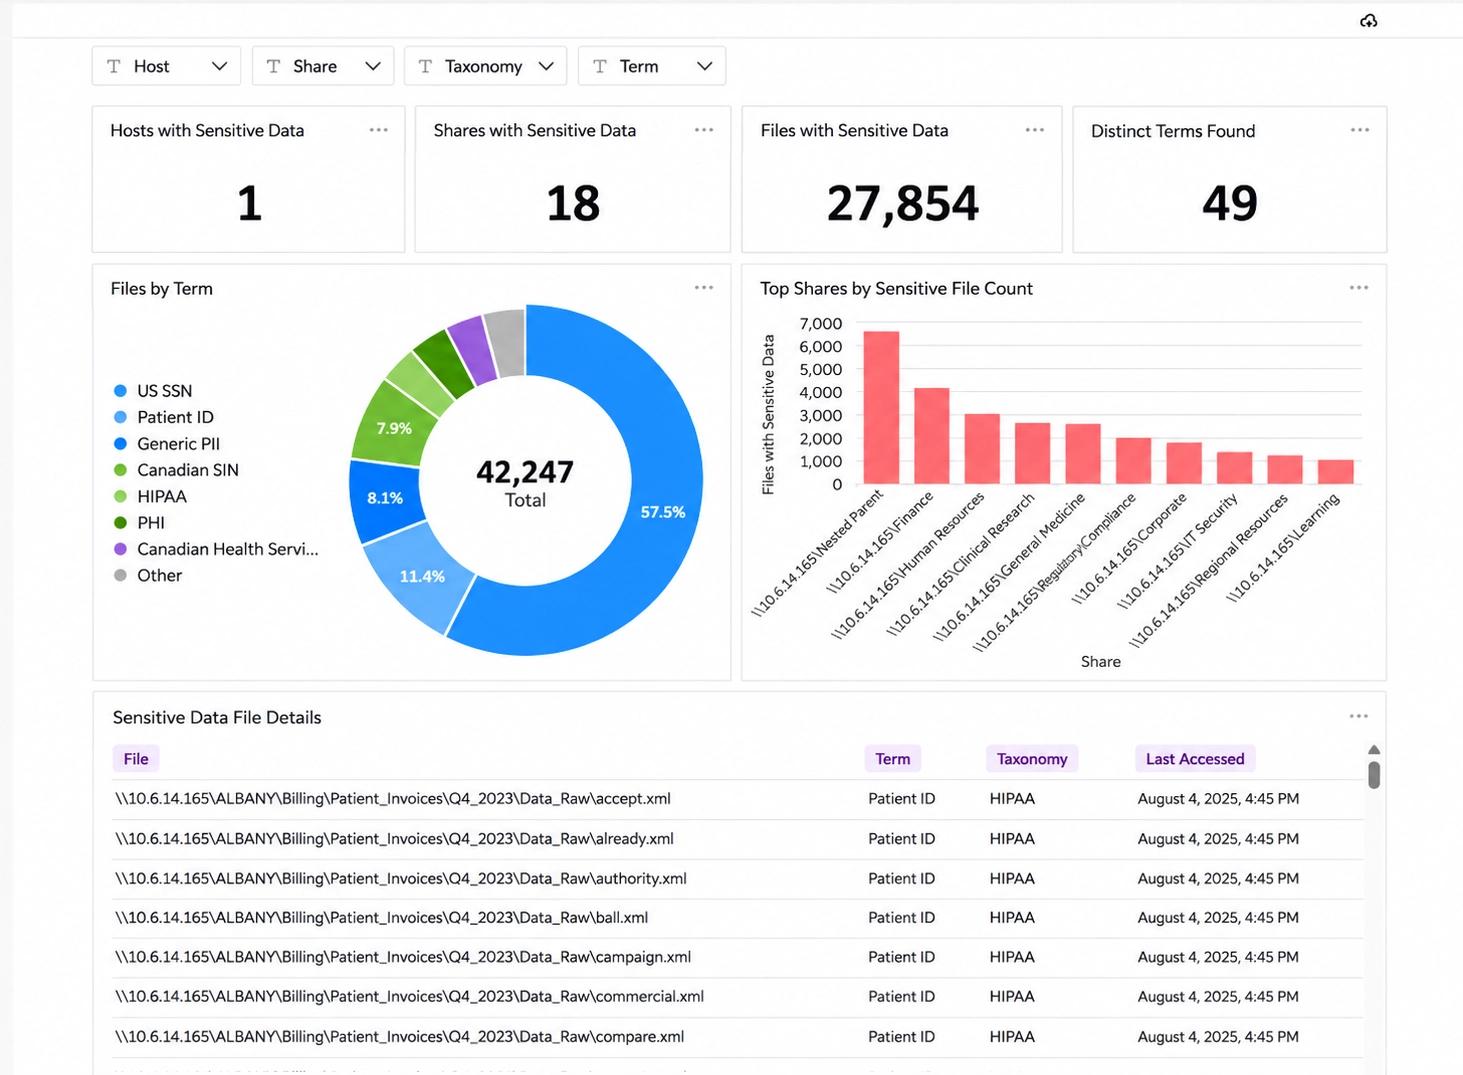
See exactly what changed, before and after
Compare before-and-after values for every modified object side by side, so improper or unauthorized changes on systems holding CUI are easy to identify.
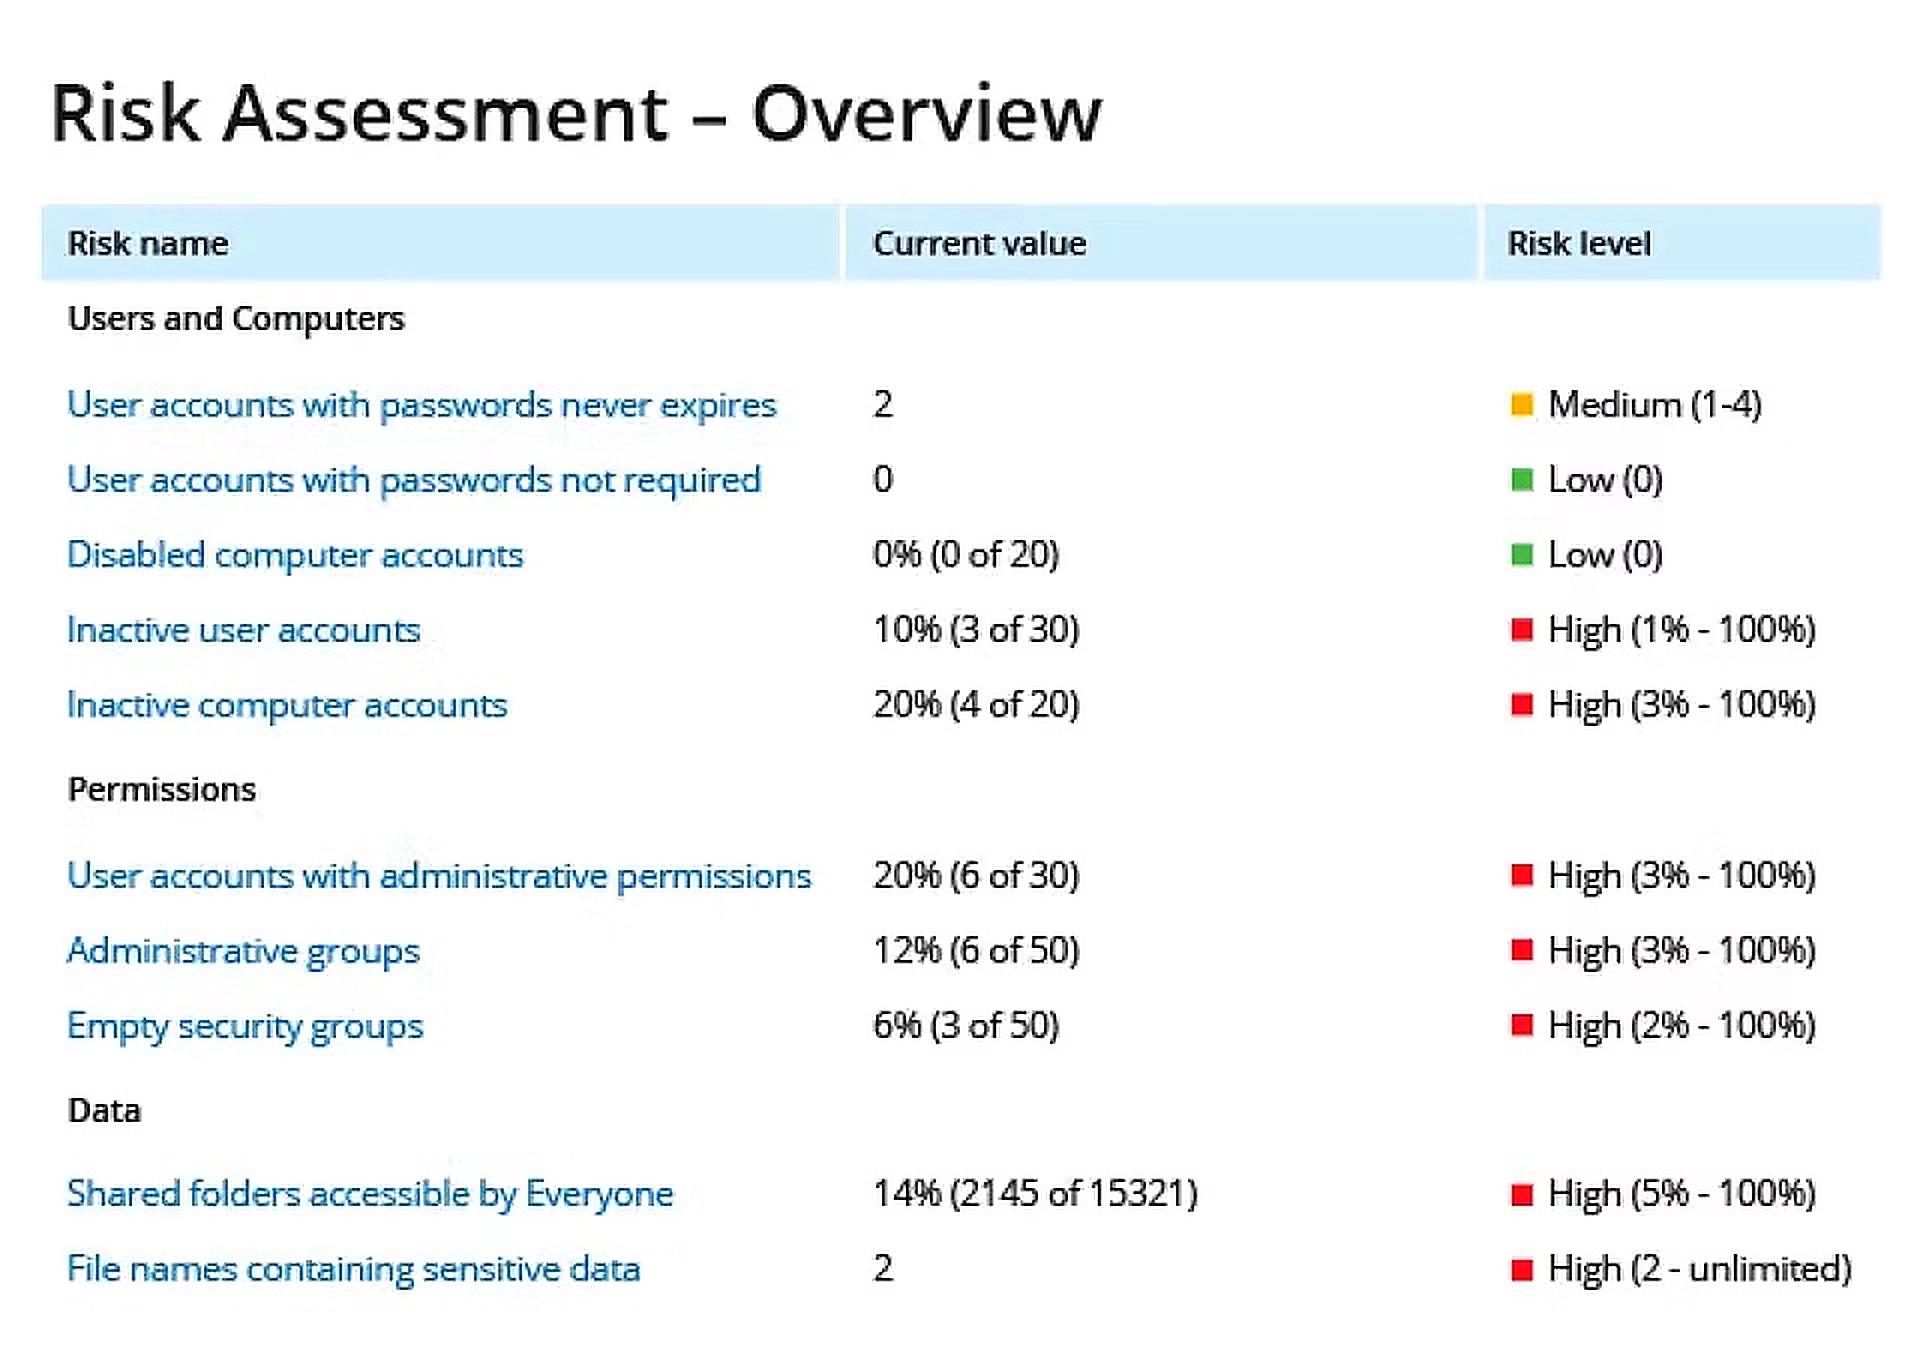
Control which devices can connect to your endpoints
Set deny, allow, or read-only rights for USB storage, printers, Bluetooth, and other devices, so CUI only moves to the people and devices you have approved.
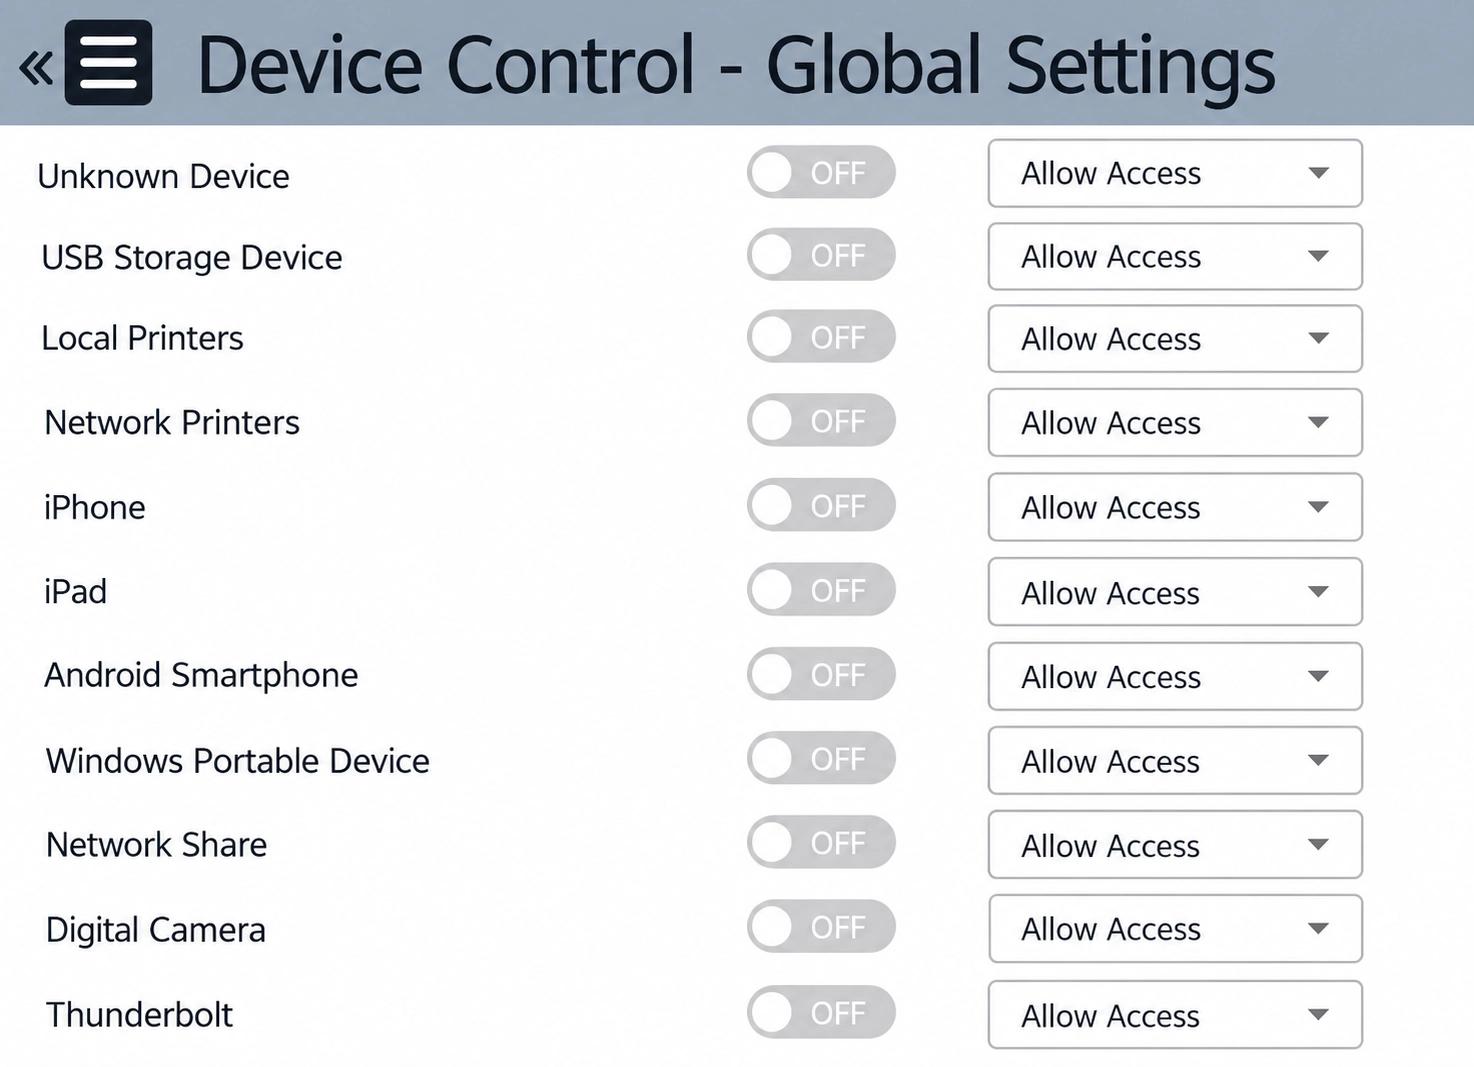
Score your Active Directory and Entra ID risk
A health check report assesses Active Directory and Entra ID against more than 170 security checks and scores the risks it finds, supporting CMMC's periodic risk assessment requirements.
Jump straight to a capability
Learn more about CMMC compliance
Webinars, guides, and articles on identifying and protecting CUI.