
Top 9 Netwrix Auditor reports for NIS2 compliance audits
Sep 18, 2026
NIS2 changes what "good enough" security looks like for a huge slice of the European economy. If your organization operates in energy, transport, finance, health, digital infrastructure, or any of the other sectors the directive designates as critical infrastructure, you can no longer choose whether to formalize your cybersecurity risk management. Instead, you have to decide how fast you can prove it.
Why NIS2 matters right now
NIS2 is the second iteration of the EU's Directive on Security of Network and Information Systems. It came into force on January 16, 2023, and the compliance deadline for affected entities passed on October 17, 2024. With that deadline passed, regulators aren’t asking for readiness anymore; they want organizations to show their work.
The directive splits affected organizations into two groups. Essential Entities include sectors like energy, transport, finance, public administration, health, space, water supply, and digital infrastructure. Important Entities cover postal services, waste management, chemicals, research, food, digital providers, and manufacturing.
What both groups have in common is Article 21, which requires appropriate technical, operational, and organizational measures across risk analysis, incident handling, business continuity, access control, and vulnerability management. You now have to show the auditor that your controls actually work instead of simply putting them in writing. Most organizations feel this gap the same way: their policies describe intent, but Article 21 is asking for evidence of who has access, what they did with it, and whether you'd notice if something went wrong. Netwrix Auditor closes that gap by collecting audit data across on-premises and cloud systems and turning it into reports that answer those exact questions, rather than leaving them for someone to reconstruct manually after the fact.
The nine reports below follow the same logic an auditor, or an attacker, would use: start with who holds power in the environment, look at what they're actually doing with it, then confirm you can prove what changed and recover if it shouldn't have.
Start with who holds power
Before you can monitor an environment, you need to know who can actually affect it. These three reports map the access surface an auditor, or an attacker, would look for first.
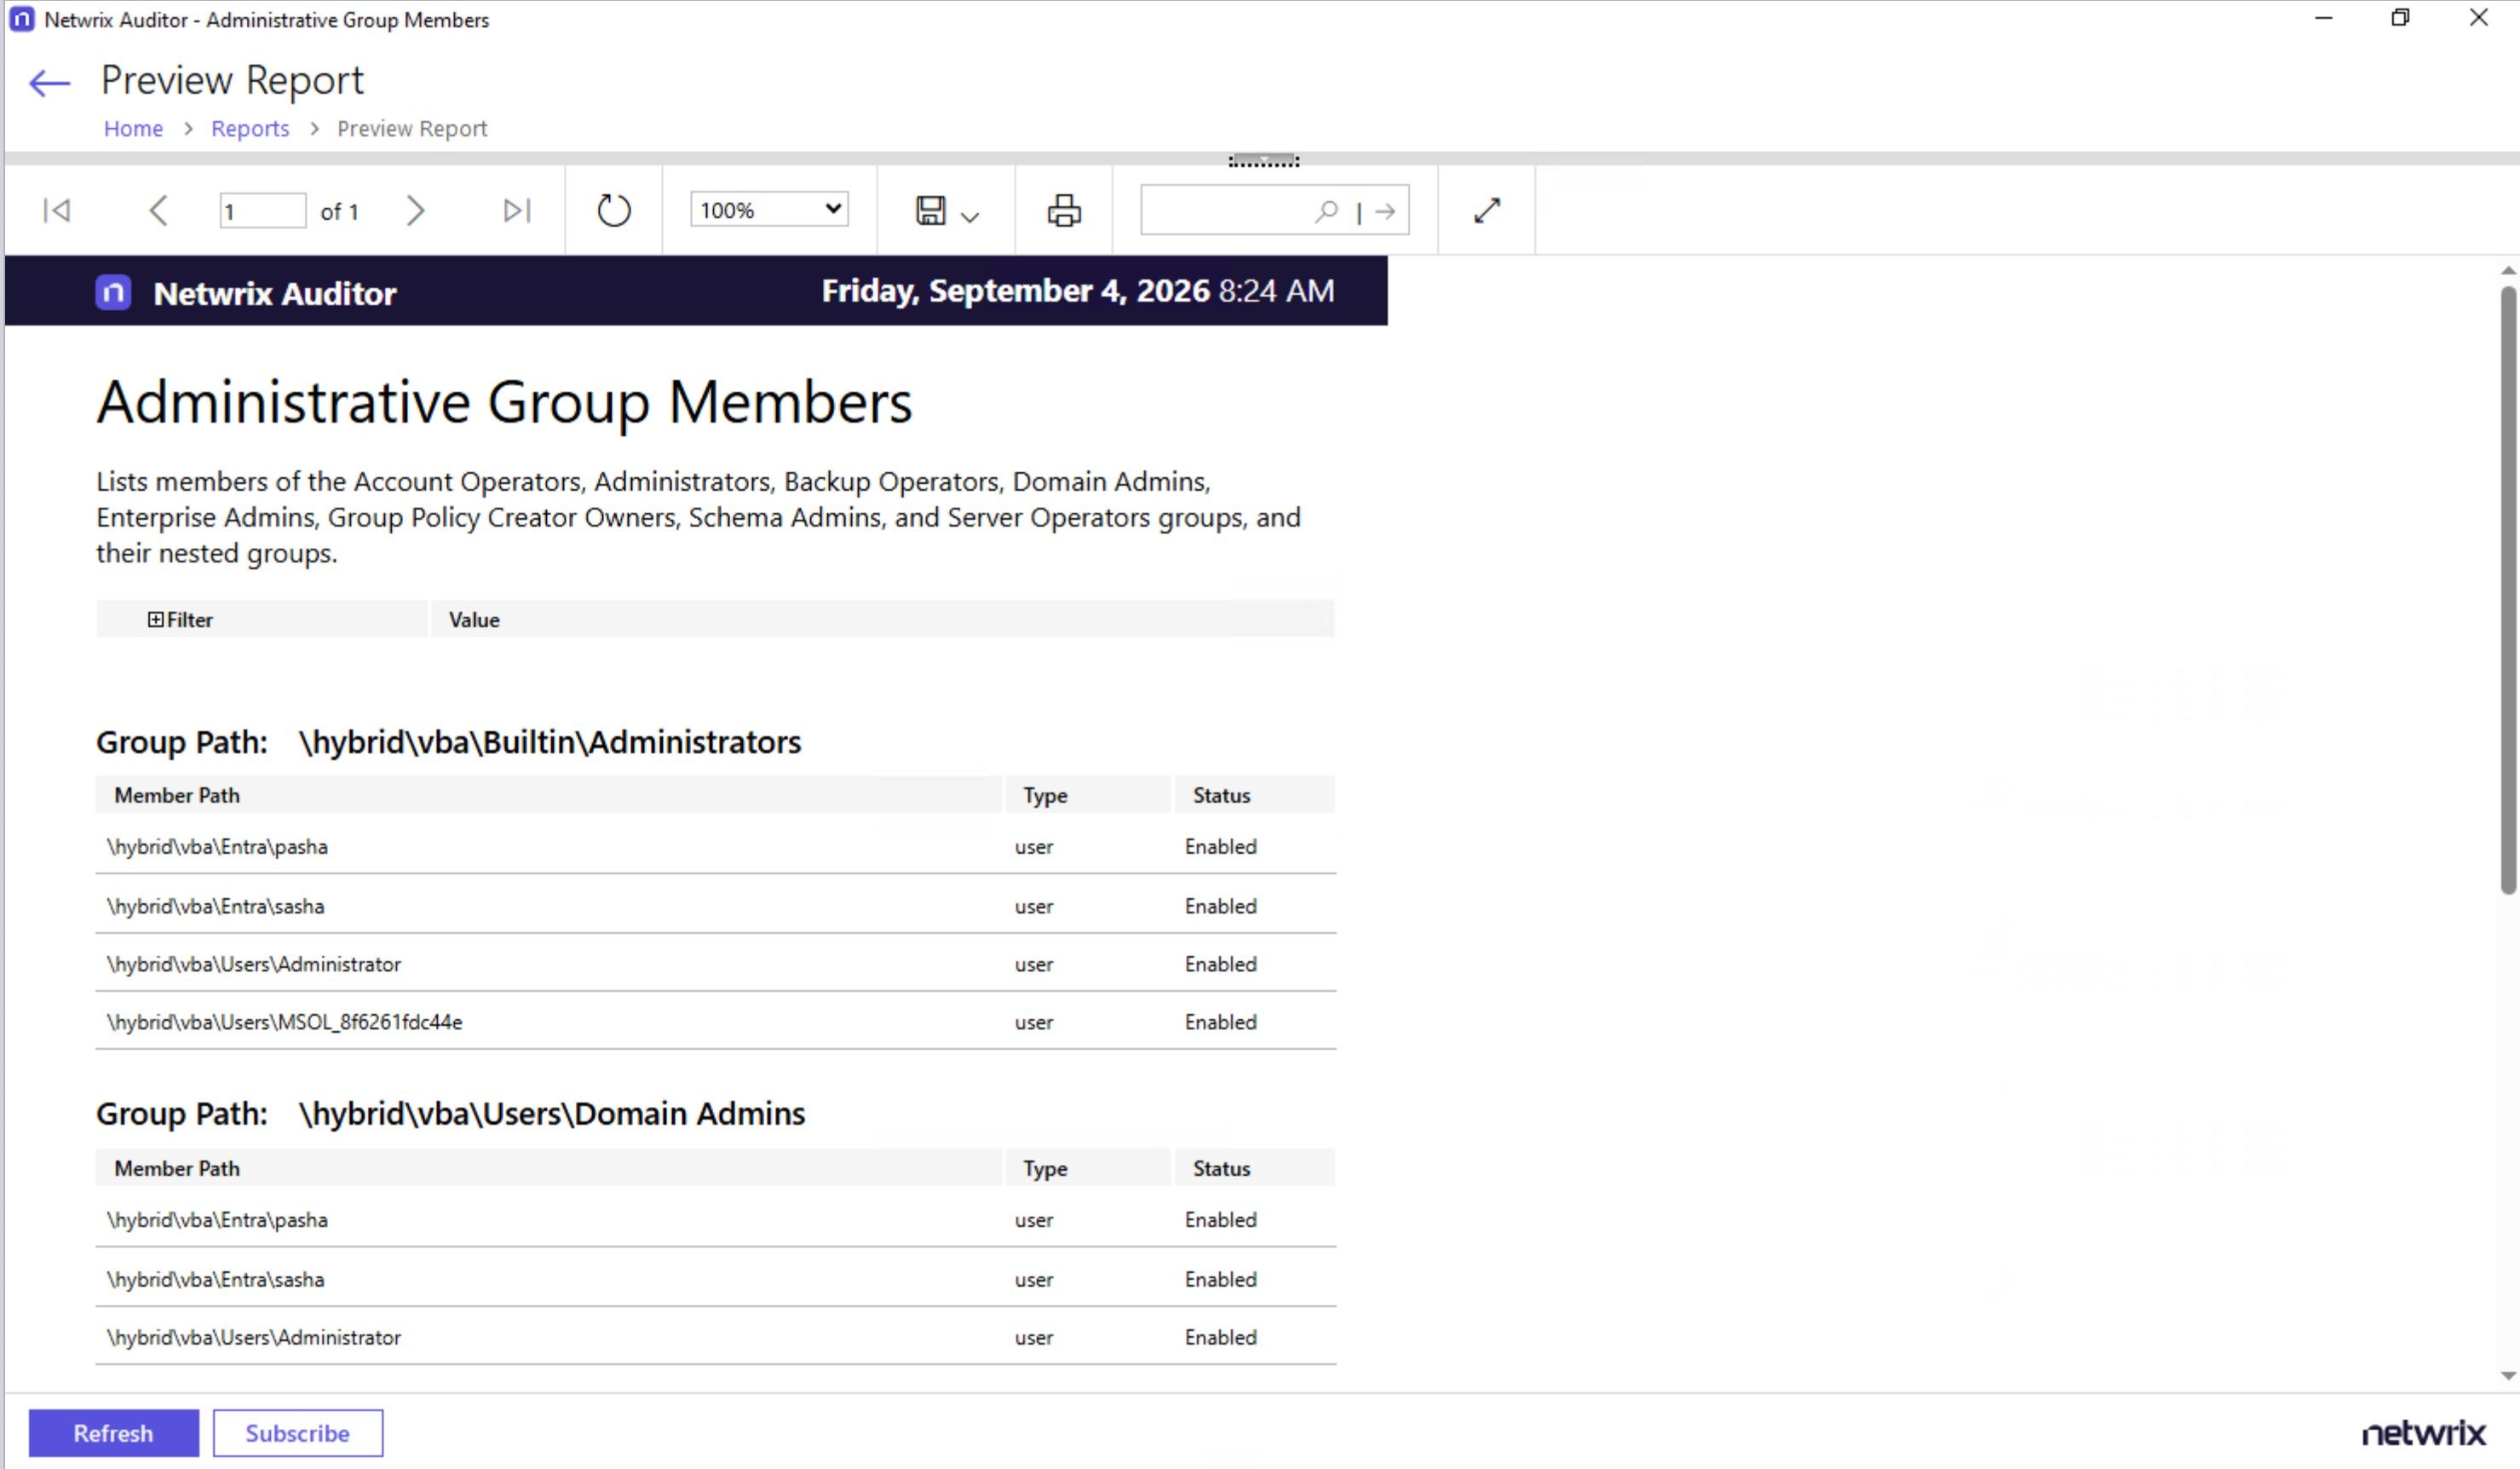
Administrative Group Members lists who belongs to your most sensitive groups, including Domain Admins, Enterprise Admins, and Account Operators, along with nested group members. If someone quietly added themselves to Domain Admins, this is where you'd find it.
Account Permissions shows which accounts have permissions on specific files and folders, whether granted directly or inherited through group membership, and flags Everyone and Authenticated Users permissions. It turns least-privilege from a policy statement into something you can verify.
Overexposed Files and Folders takes that a step further by identifying sensitive files and folders that specific users or groups can reach based on the combined effect of folder and share permissions. This report shows you both who has access and what’s exposed as a result.
Then watch what they do with it
Access without oversight is exactly what NIS2's monitoring requirements are meant to prevent. These four Netwrix Auditor reports track behavior once accounts and permissions are in place.
User Account Changes captures every account lifecycle event: creation, modification, and deletion. It's the baseline record for catching accounts that were created or elevated without proper approval.
All Logon Activity covers interactive and non-interactive logons, successful and failed, in a single view. It's core evidence for access control and monitoring, and often the first place investigators look when something has gone wrong.
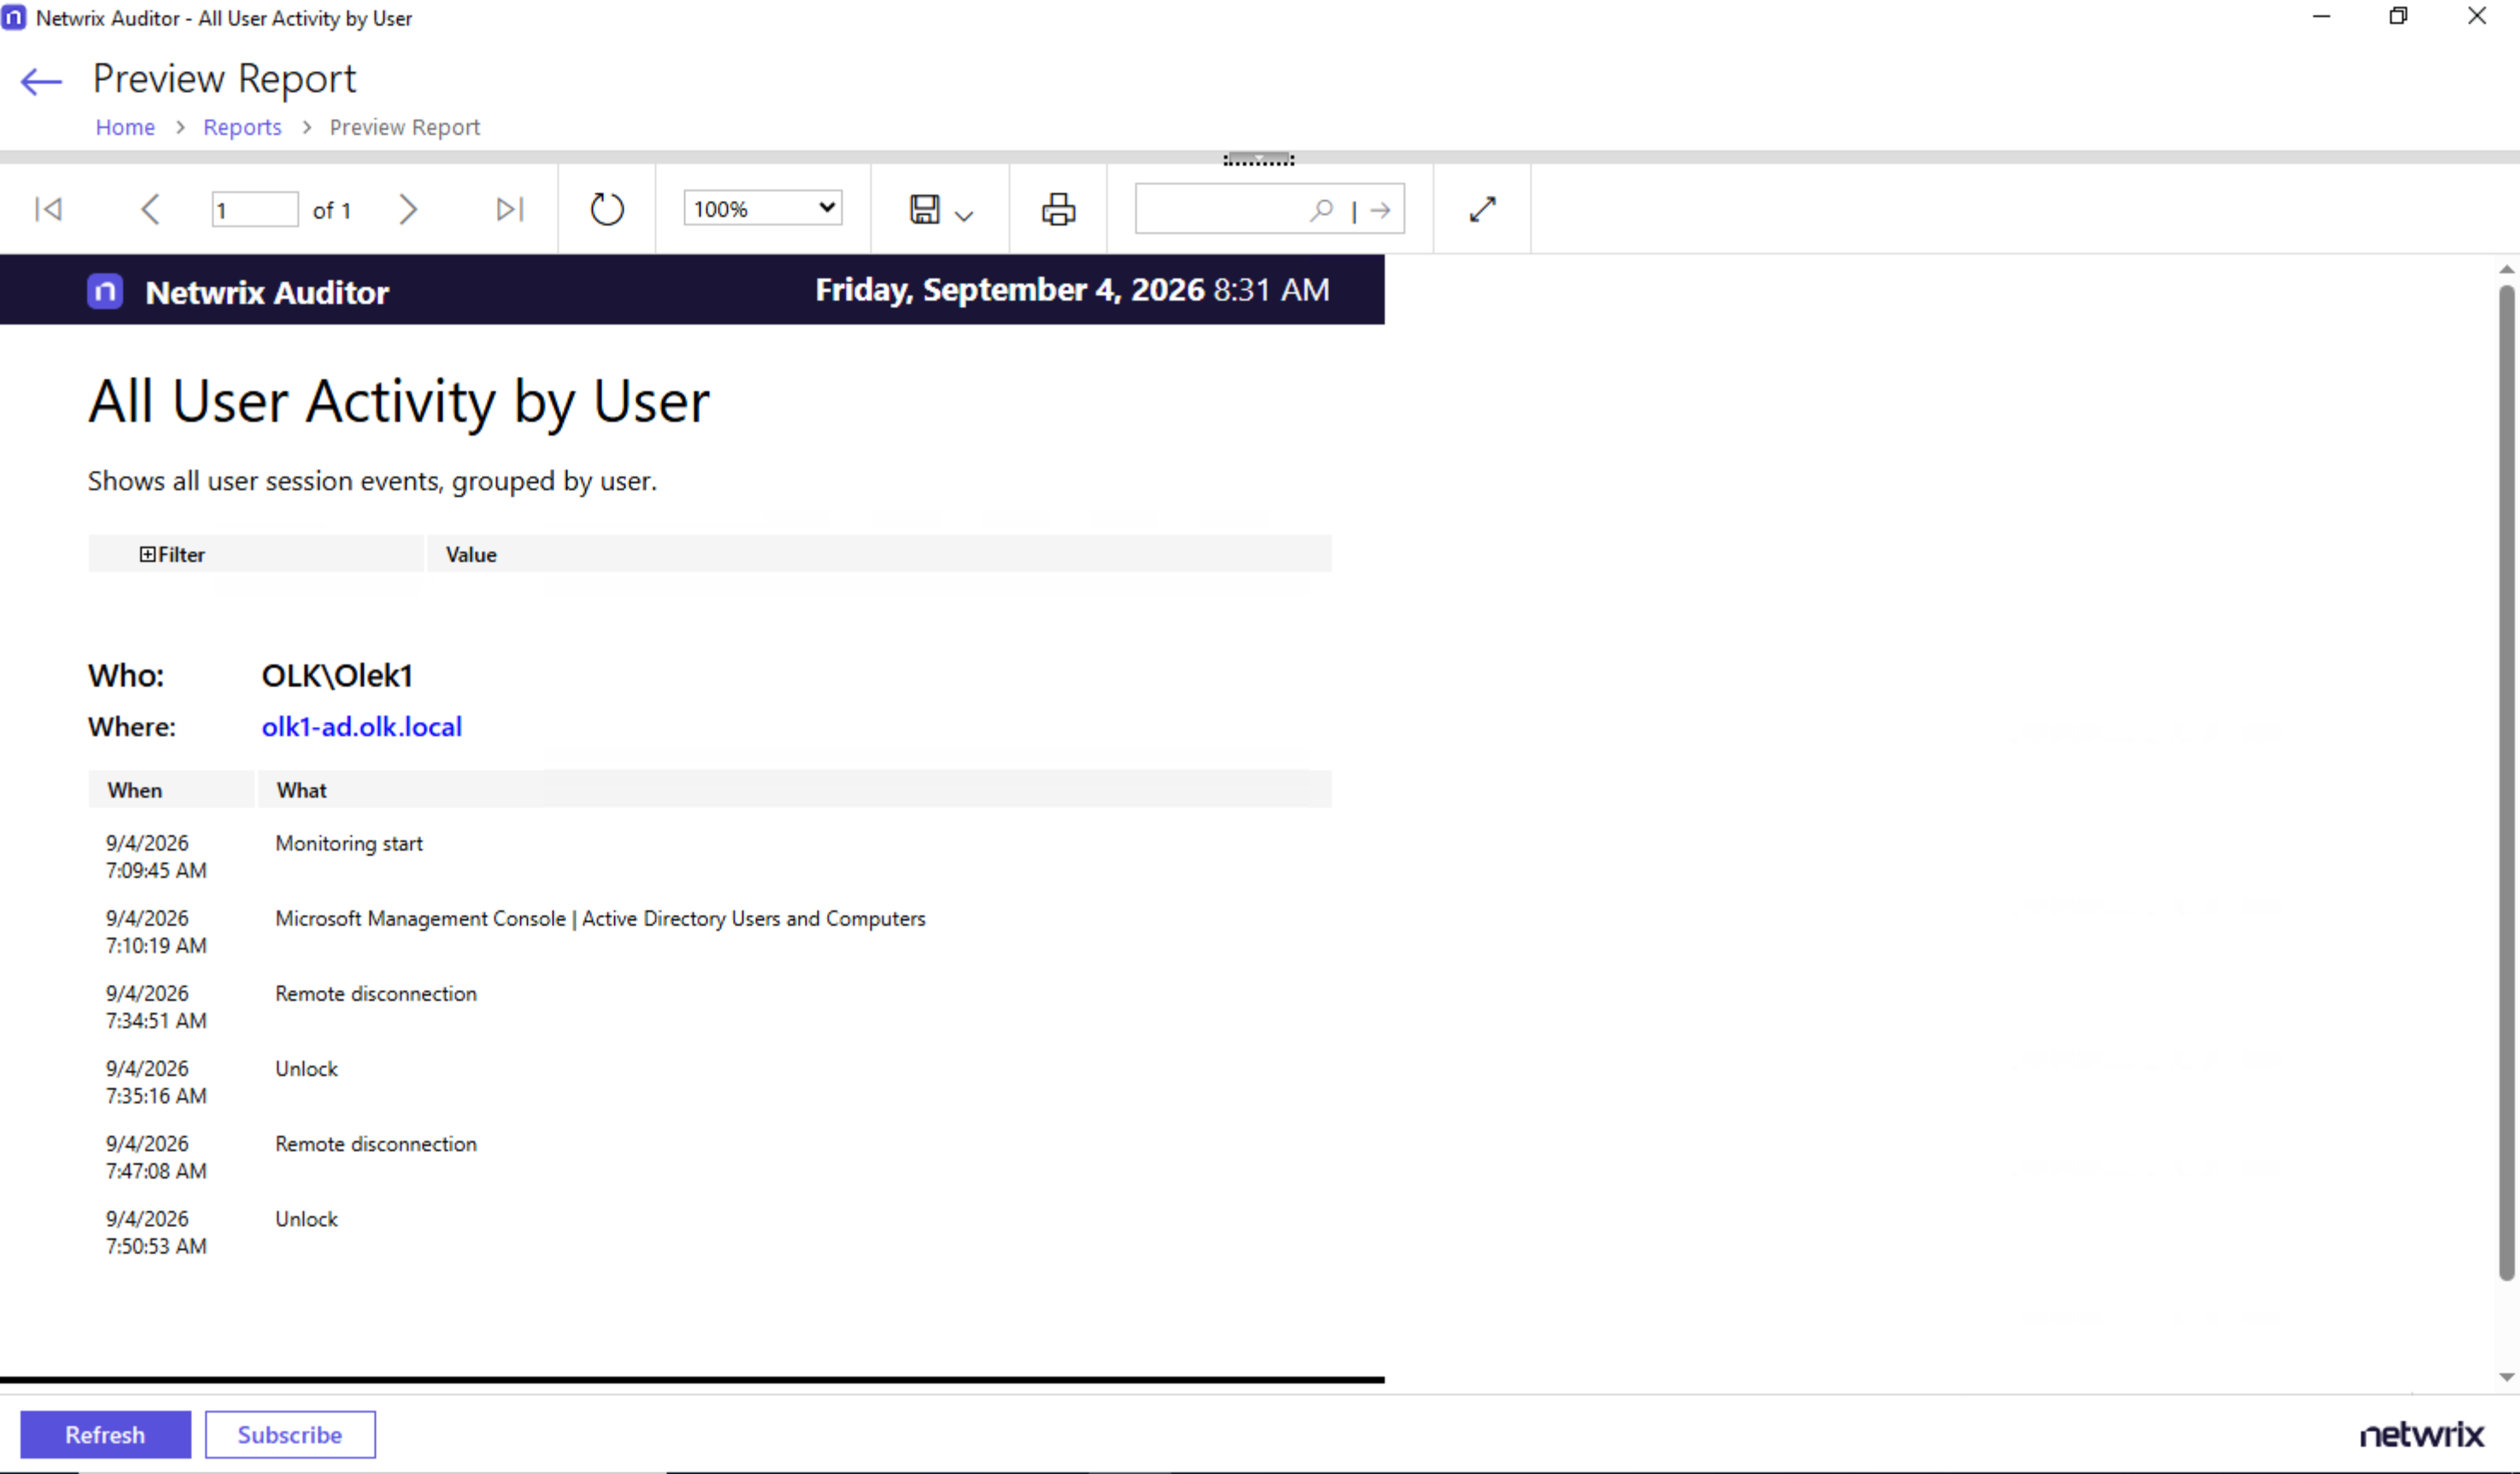
All User Activity by User builds on that with session-level activity for each account across the environment, giving you a complete behavioral picture to support incident investigation and ongoing risk assessment.
All Changes by User rolls all of that up further, showing every change across your IT infrastructure grouped by the person who made it andwho touched what and when, in a single view instead of multiple different reports.
Finally, prove what changed and that you can recover
Article 21 doesn't stop at prevention. It also expects you to show that changes are tracked and that you can restore what's lost. These two Netwrix Auditor reports close that loop.
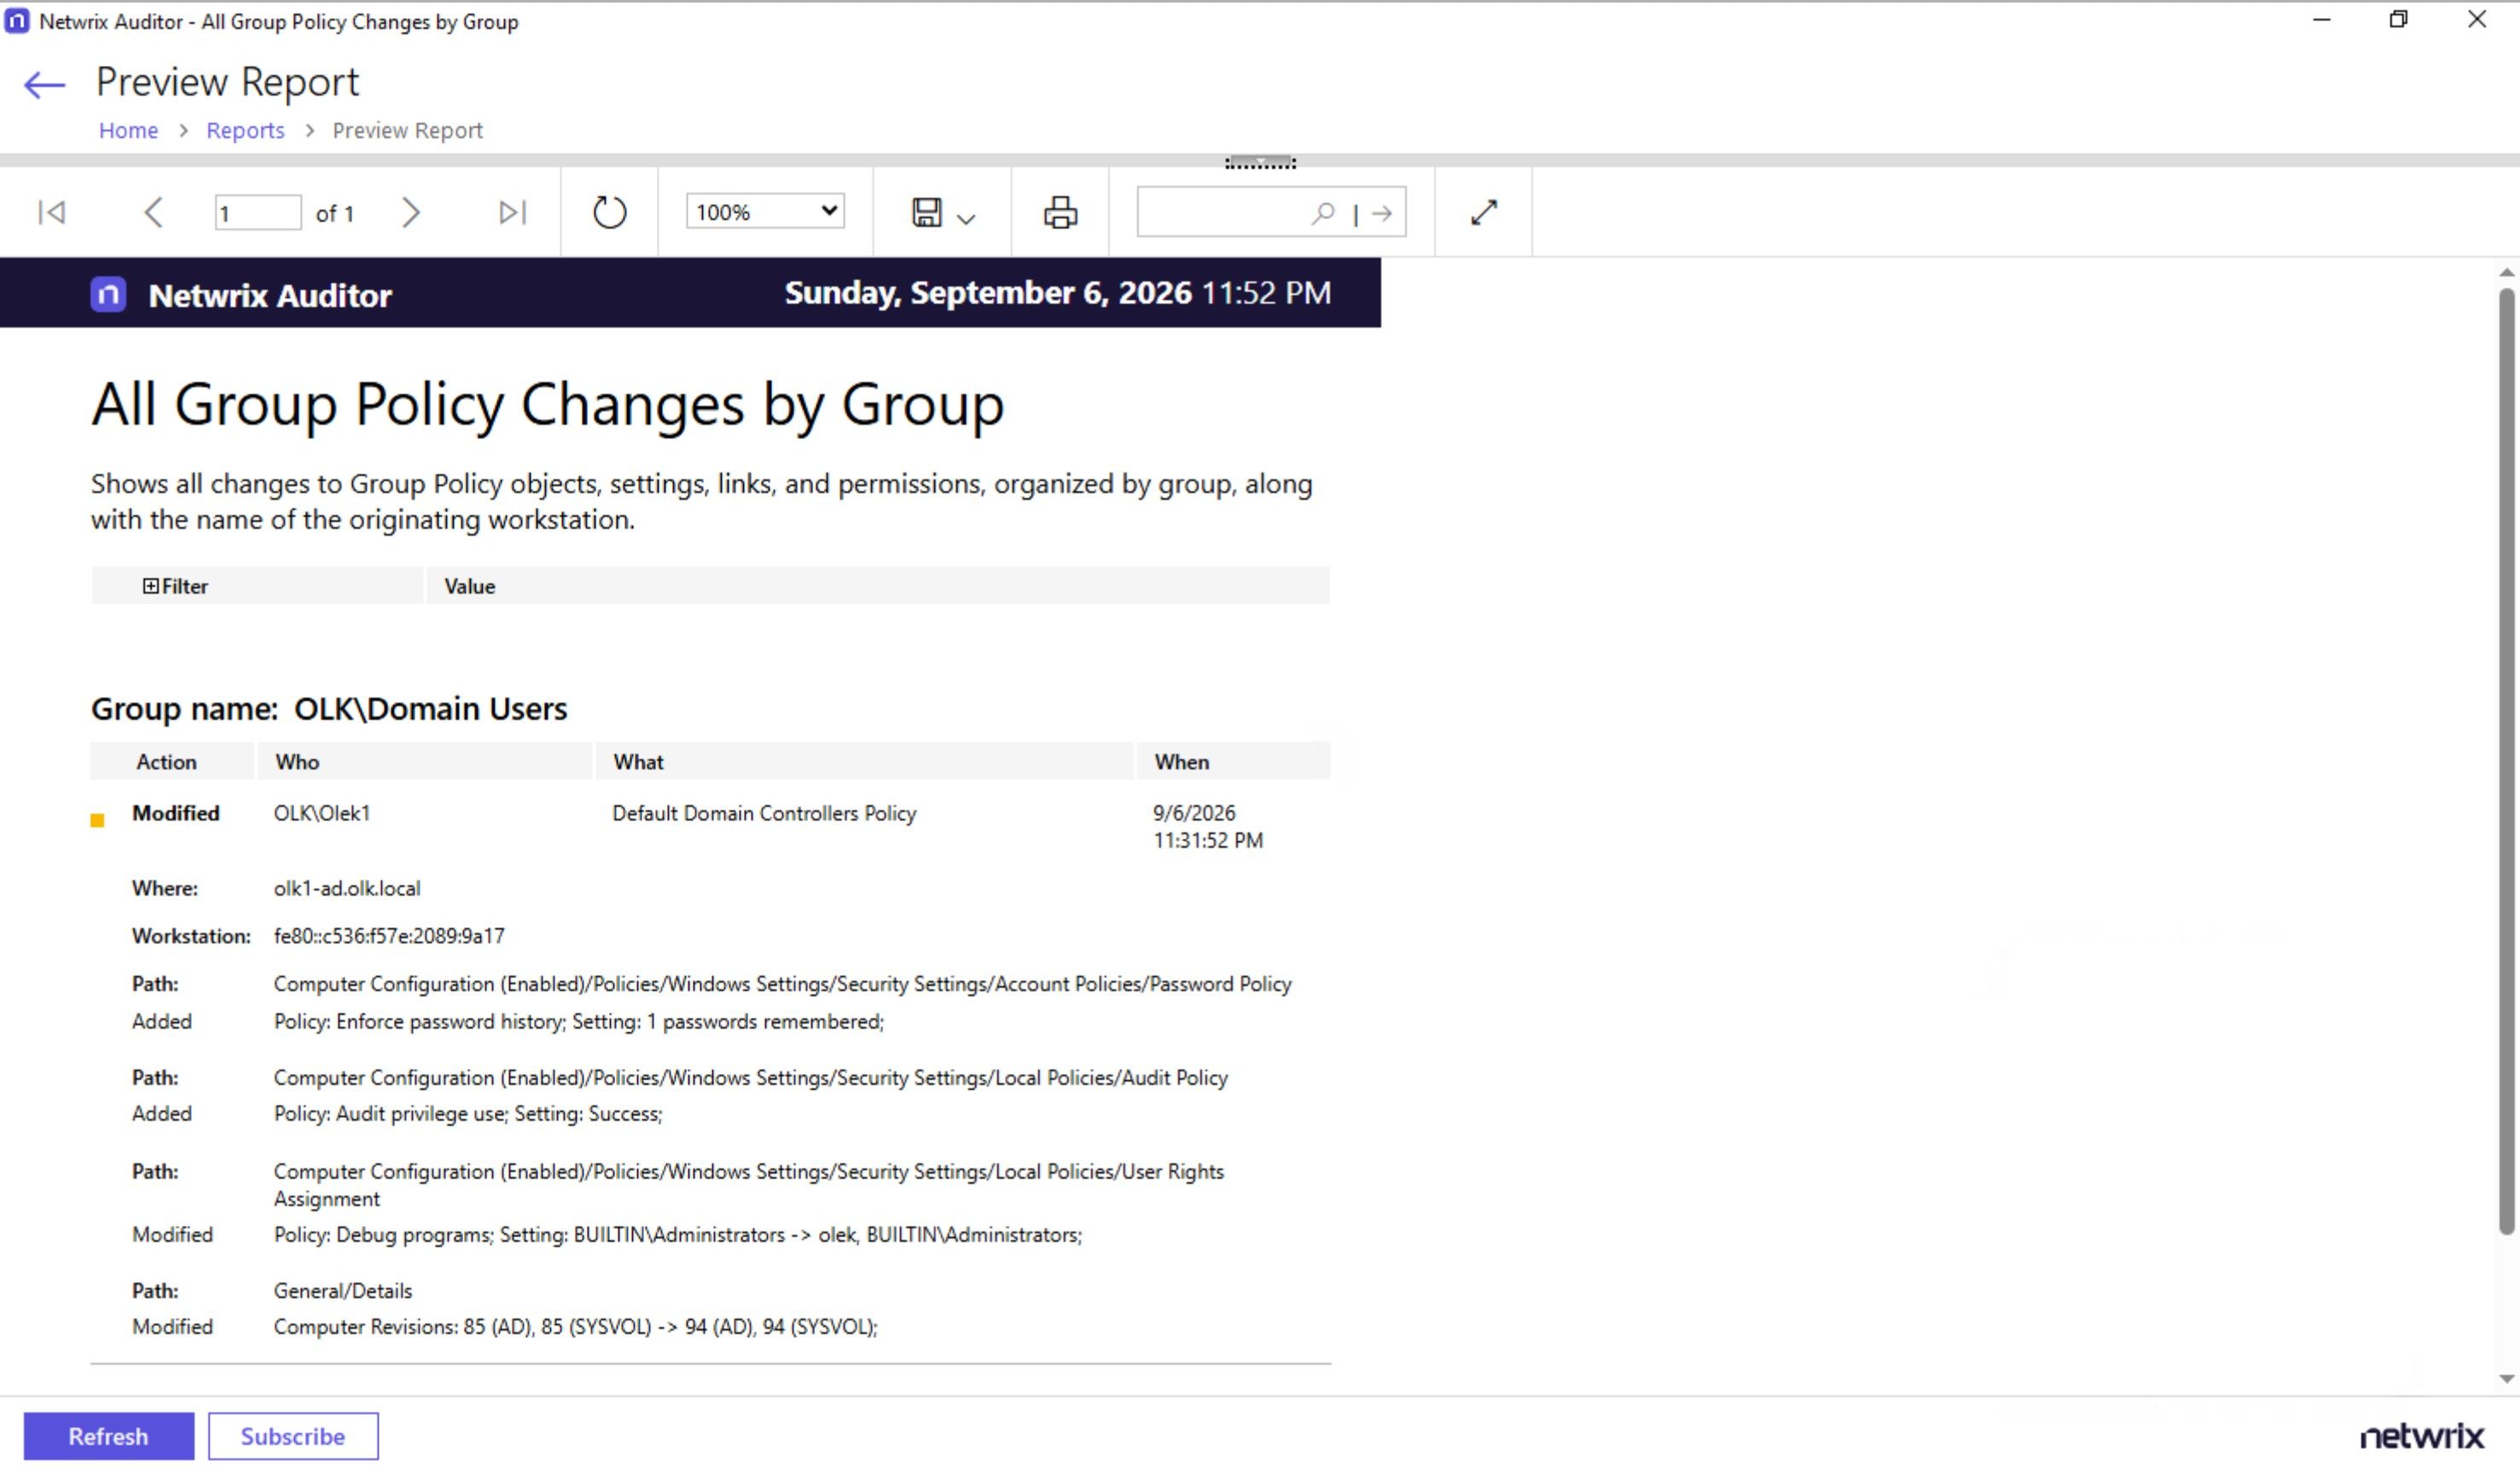
All Group Policy Changes by Group tracks every change to GPOs, settings, links, and permissions, along with the originating workstation, so unauthorized policy changes don't sit undetected. Group Policy touches password requirements, software restrictions, and a large share of your overall security posture, which makes its change history worth watching closely.
Files and Folders Deleted captures deleted files and folders along with their attributes, supporting both recovery efforts and the investigation required by NIS2's business continuity and incident handling rules.
Together, these nine reports answer the questions an audit typically asks: who can act, what they did, and whether you can prove and reverse it.
Beyond Auditor: a broader NIS2 toolkit
Netwrix Auditor covers a lot of ground, but NIS2 compliance touches more than audit trails and reporting. It also asks you to protect your sensitive data, enforce secure authentication, and keep access under control, which is where Netwrix's other solutions come in. Netwrix Data Classification helps you find and label sensitive data across your environment so you know what requires the strongest protection. Netwrix Password Policy Enforcer strengthens the authentication controls Article 21 calls out directly, and Netwrix Directory Manager helps keep group membership and access policies consistent and intentional across Active Directory and Entra ID, rather than left to sprawl. Used together, these products give essential and important entities a much more complete answer to what NIS2 asks for: evidence, control, and the ability to respond fast when something goes wrong.
NIS2 sets an ongoing expectation that you’ll be able to see what's happening in your environment and prove it on demand. The reports above are a solid starting point, but the real value comes from building them into a routine, not pulling them together the week before an audit.
Share on
Learn More
About the author
Daniel Bago
Product Marketing Manager
Daniel Bago is a product marketing manager at Netwrix, responsible for the Data Security Posture Management solution and data security products such as Netwrix Auditor, Netwrix Access Analyzer, and Netwrix 1Secure. An avid technology enthusiast, he has supported the communication activities of leading technology companies, including Microsoft, Google, Intel, IBM, and Lenovo, and has held product marketing roles at various cybersecurity and biotechnology companies.